API Integration Explained: How Different Business Systems Work Together
Learn how APIs enable business systems to exchange data, what to plan before connecting them, and how to build integrations that handle security, failures, retries, and reconciliation.
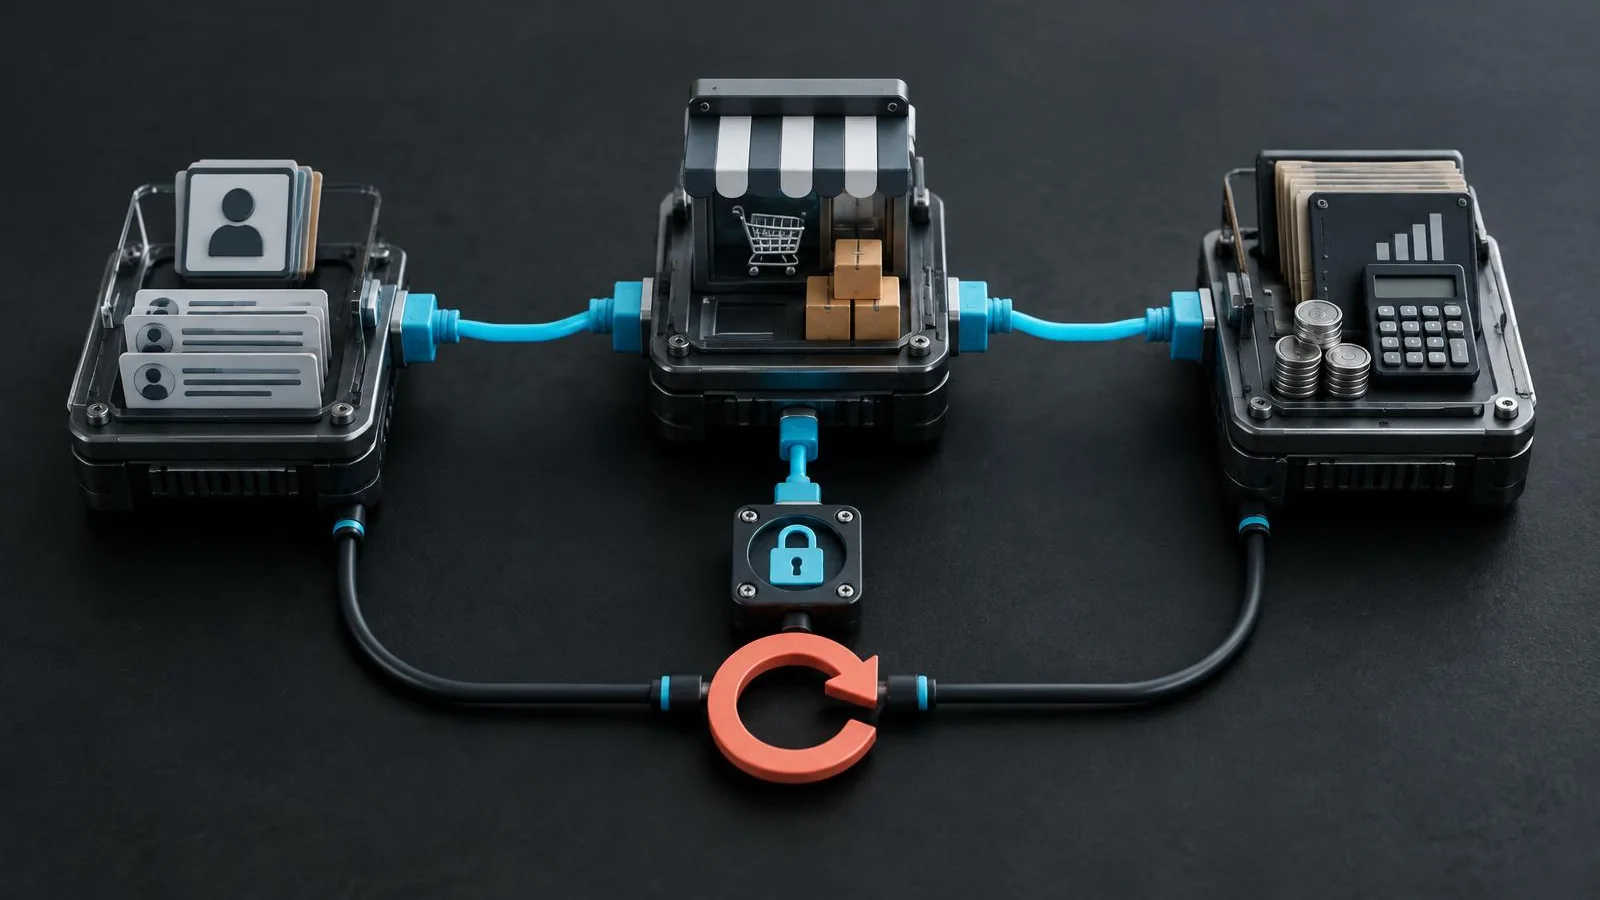
Most businesses rely on several digital systems: a website, customer relationship management platform, accounting software, booking tool, ecommerce store, or email service. When these systems cannot share information cleanly, staff may copy data by hand, repeat tasks, or work from conflicting records. API integration connects applications through defined interfaces so they can exchange information and trigger actions.
An API is not magic glue. Integrations need clear ownership of data, permission boundaries, validation, error handling, and a way to recover when services are unavailable. This guide explains common integration patterns and a practical planning workflow, including least-privilege access, idempotency, retries, and reconciliation. Any scenarios below are explicitly hypothetical and illustrate concepts rather than promising a particular efficiency gain.
What API integration means
An application programming interface (API) is a defined way for software to request data or actions from another system. An integration uses one or more APIs to move information or coordinate a workflow. For example, a website might send a submitted lead to a CRM, or an order system might pass payment status to an accounting platform.
Define the workflow and source of truth
Begin with the business process, not the API endpoint. Map who creates or updates information, which systems need it, and what should happen when information changes. Define the fields involved, including formats, required values, and identifiers. Determine which system is authoritative for each field. Without that decision, two systems can overwrite each other or present different versions to staff.
- Name the event that starts the workflow and the expected outcome.
- Identify the records and fields that move in each direction.
- Assign an authoritative system for each important data element.
- Define how duplicates, corrections, deletions, and consent changes are handled.
- List the people or teams who own the workflow and support incidents.
Choose a suitable integration pattern
Direct request and response
A direct integration sends a request to another system and processes its response. This can work for a straightforward task where the user needs immediate confirmation. It also means the user-facing workflow may depend on the external service being available and responsive. Set appropriate timeouts and provide a clear failure state rather than leaving a page to wait indefinitely.
Queued or asynchronous processing
For work that can complete later, a queue can separate the initial user action from downstream processing. The system records a job, acknowledges the request appropriately, and processes it in the background. This can make failure handling more manageable, but requires monitoring, retry rules, and a way to report delayed or permanently failed jobs.
Webhooks and scheduled synchronization
A webhook lets a provider notify another system when an event occurs, while scheduled synchronization periodically checks for updates. Webhooks can reduce delay but require verification, replay protection, and careful handling of repeated or out-of-order notifications. Scheduled polling may be easier where webhooks are unavailable, but must respect rate limits and avoid unnecessary requests.
Use least privilege and protect credentials
Integration credentials are keys to business data and operations. Use a dedicated account or service identity where supported, grant only the permissions the workflow needs, and avoid sharing administrator credentials. Store secrets in an appropriate secret-management facility or protected server configuration—not in browser code, public repositories, or client-visible pages. Rotate credentials using a documented process and revoke them when access is no longer needed.
Validate the identity and authorization of incoming requests, especially webhooks. Do not trust that a request is genuine simply because it contains a familiar field or URL. Use the provider’s supported signature or authentication method, protect against replay where relevant, and apply access controls to any internal endpoints. Keep logs useful for investigation while avoiding unnecessary exposure of personal or confidential data.
Validate and transform data at the boundary
Applications often represent the same concept differently. A phone number, address, date, currency, or status may require transformation before another system can use it. Define accepted values and formats, validate incoming and outgoing data, and reject or quarantine records that do not meet the agreed rules. Do not silently substitute important business information with a default that could be mistaken for a real value.
Validation should cover required fields, lengths, data types, allowed values, and relationships between fields. Normalize only where it is safe and documented. For example, a date without a timezone may be ambiguous; a status label in one platform may not correspond exactly to a status in another. Maintain a mapping that can be reviewed when either system changes.
Design retries, idempotency, and reconciliation
Networks fail. A request may reach a provider even if the caller times out before receiving the response. If the caller blindly repeats an operation, it could create duplicate contacts, orders, or payments. Idempotency means that repeating a request with the same operation identity has a controlled effect rather than unintentionally performing the action again. Use provider-supported idempotency keys where available, or design a reliable deduplication method around stable identifiers.
Retry only errors that are likely to be temporary, and follow the provider’s guidance on rate limits and backoff. Repeated rapid requests can worsen an outage or violate API limits. Set a retry limit, add a delay that grows appropriately between attempts, and distinguish temporary failures from invalid data, permission errors, or unsupported requests. Those permanent failures usually need correction rather than repetition.
A retry strategy is not a substitute for reconciliation. A scheduled reconciliation can compare relevant records or transaction states between systems and identify missing, duplicated, or out-of-sync data. Define which system wins when differences appear, who reviews exceptions, and how a correction is recorded. Reconciliation is especially important for asynchronous workflows and high-consequence operations.
Test and monitor the integration
Test successful flows as well as failure conditions. Use a provider sandbox where available, and avoid testing with real customer data or live transactions unless the process is explicitly approved. Cover missing fields, invalid values, expired credentials, timeouts, rate limits, duplicate events, delayed webhooks, partial failures, and provider maintenance. Confirm how the integration behaves when only some steps succeed.
- 1Document the workflow, data ownership, field mapping, and expected outcomes.
- 2Build a small end-to-end test with representative but non-sensitive data.
- 3Simulate timeouts, invalid inputs, duplicate events, and unavailable services.
- 4Verify logs, alerts, retry limits, and the operator’s recovery instructions.
- 5Deploy through a controlled release process and confirm production behavior.
- 6Review failures and reconciliation reports regularly; update the integration when APIs change.
Monitoring should make important failures visible without generating so much noise that teams ignore alerts. Track request outcomes, processing delays, queue depth, rate-limit responses, and unresolved records as appropriate. Include a correlation identifier that connects application logs and provider activity. Assign an owner who can investigate alerts and communicate with the business team.
Plan your development priorities
Need help with your digital growth? Let's talk about your project.
Discuss your projectKey takeaways
- Map the business workflow and define each system’s source of truth before connecting APIs.
- Choose a synchronous, asynchronous, webhook, or scheduled approach based on user needs and provider behavior.
- Protect credentials and use least-privilege access; validate and minimize the data exchanged.
- Plan idempotency, bounded retries, rate-limit handling, and reconciliation to manage failures and duplicates.
- Test failure cases, monitor operations, and assign long-term ownership for provider and API changes.
Frequently asked questions
API integration is a way for software systems to exchange data or request actions through documented interfaces. It can connect workflows such as website enquiries and CRM records, provided the systems’ APIs and business rules support the required behavior.
Conclusion
API integration can reduce disconnected work when it is built around a clearly defined process and supported with robust safeguards. Define ownership and data rules first, then select a suitable pattern and engineer for least privilege, validation, idempotency, controlled retries, and reconciliation. Those practices make failures easier to detect and resolve rather than allowing silent data drift.
For help planning or building connected digital systems, explore our web development services. See also our Prototech project example and WordPress website SEO checklist. Need help with your digital growth? Let's talk about your project. Discuss your project.
Want this done for you?
Book a free strategy call and we will review your site, your search visibility and your ad accounts, then tell you the three highest-impact things to fix first.
About the author
Gurpreet leads strategy and delivery at CSSHouse Consulting, where he has spent the last decade building websites and search programs for service businesses, SaaS teams and ecommerce brands across India, the UK and North America.
Work with our teamRelated articles
How to Improve WordPress Website Speed and Core Web Vitals
A practical WordPress performance guide to identifying slowdowns, improving theme and plugin efficiency, configuring caching safely, and testing changes without disrupting a live website.
Progressive Web Apps (PWA): Benefits, Features, and Business Use Cases
Understand what progressive web apps can offer, where they fit alongside websites and native apps, and how to plan a PWA around real user needs and platform constraints.
WordPress Website: Make Sure SEO Is Part of the Plan
WordPress website SEO is easier to support when page structure, content and measurement are part of the initial plan. Adding a plugin after launch cannot repair a confusing service structure or missing information on its own.